

Your 2027 Cyber Budget Is Probably Funding the Wrong Things


Every year, security budgets get approved on a familiar list: new tools, renewed licences and leftover projects. And every year, organisations are breached through gaps that list never covered.
As boards finalise their 2027 budgets, security leaders need to answer one question: if a serious cyber incident hit tomorrow, which of these investments would help the organisation withstand it and recover?
AI is changing both attack and defence. Skills are scarce, third-party ecosystems keep growing, and boards and regulators want more proof of resilience. Adding projects won’t fix this. Leaders have to make hard choices.
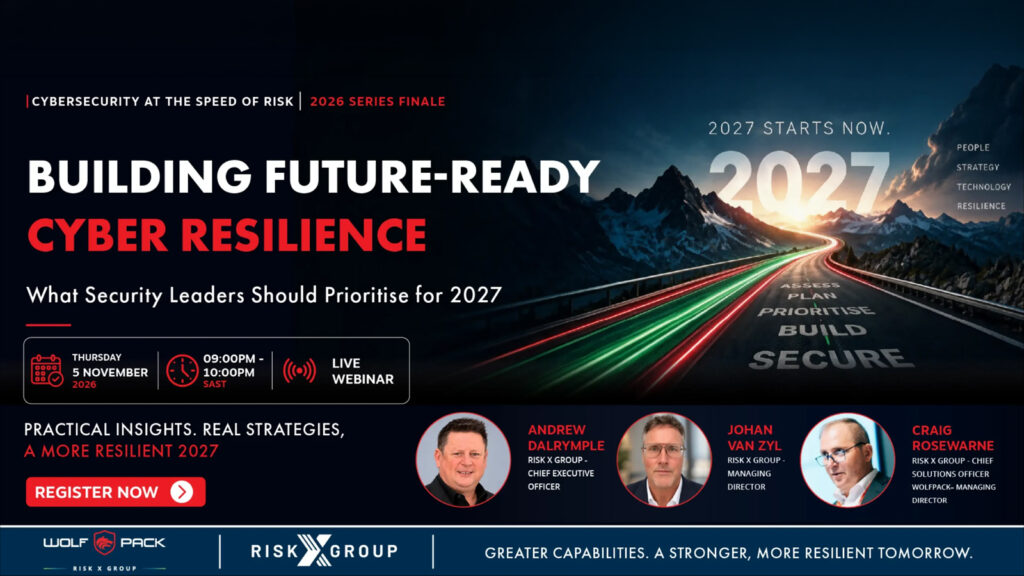
On Thursday, 5 November 2026, Wolfpack and Risk X Group will tackle those choices in the final edition of their Cyber Security at the Speed of Risk series: Building Future-Ready Cyber Resilience: What Security Leaders Should Prioritise for 2027.
Craig Rosewarne, Chief Solutions Officer; Andrew Dalrymple, Group CEO; and Johan Van Zyl, Chief Operations Officer, will share what 2026 taught the industry, where organisations should focus over the next 12–18 months, and what they should stop doing.
What the session will cover
- Start with what you can’t afford to lose. Identify the services, data and suppliers your business depends on most, and which controls are proven rather than assumed. That’s how you link every rand to a real risk and defend your priorities to the board.
- Give AI a job, or it will create one for you. AI without a clear purpose adds to your attack surface. Decide where it improves capability, what it can access and who checks its outputs.
- Build, buy or borrow your skills. Tools without the people to run them are an expensive mistake. Decide what stays in-house, where teams can grow, and where virtual CISOs, Cyber Associates or external experts fill the gaps.
- Your controls work. Do they work together? Testing should drive remediation, detection should trigger a rehearsed response, and recovery plans should be exercised. Individual controls offer limited assurance if no one has tested them together under pressure.
Leave with a roadmap
Attendees will get a practical framework for setting their own 2027 priorities, plus the 2027 Cyber Resilience Planning Checklist. It covers governance, skills, AI, offensive security, detection and response, third-party risk, resilience and human risk.
The session will also explain what Wolfpack’s acquisition by Risk X Group means for clients, including access to strategic advisory, human risk, specialist skills, offensive security and managed cyber defence.
Don’t sign off your 2027 plan before you’ve tuned in
Building Future-Ready Cyber Resilience: What Security Leaders Should Prioritise for 2027
- Date: Thursday, 5 November 2026
- Time: 9–10am SAST
- Format: Live webinar
- Speakers: Andrew Dalrymple, Craig Rosewarne and Johan Van Zyl
- Click here to register
2027 starts now. Reserve your place and begin shaping your organisation’s cyber resilience roadmap
2027 starts now. Reserve your place.





 Loading ...